How Internal Audit Software Changes Evidence and Oversight
Evidence quality changes how audit findings are trusted. This guide explains how better audit evidence reshapes oversight, strengthens Salesforce renewal decisions and helps finance, IT and procurement challenge spend with more confidence.
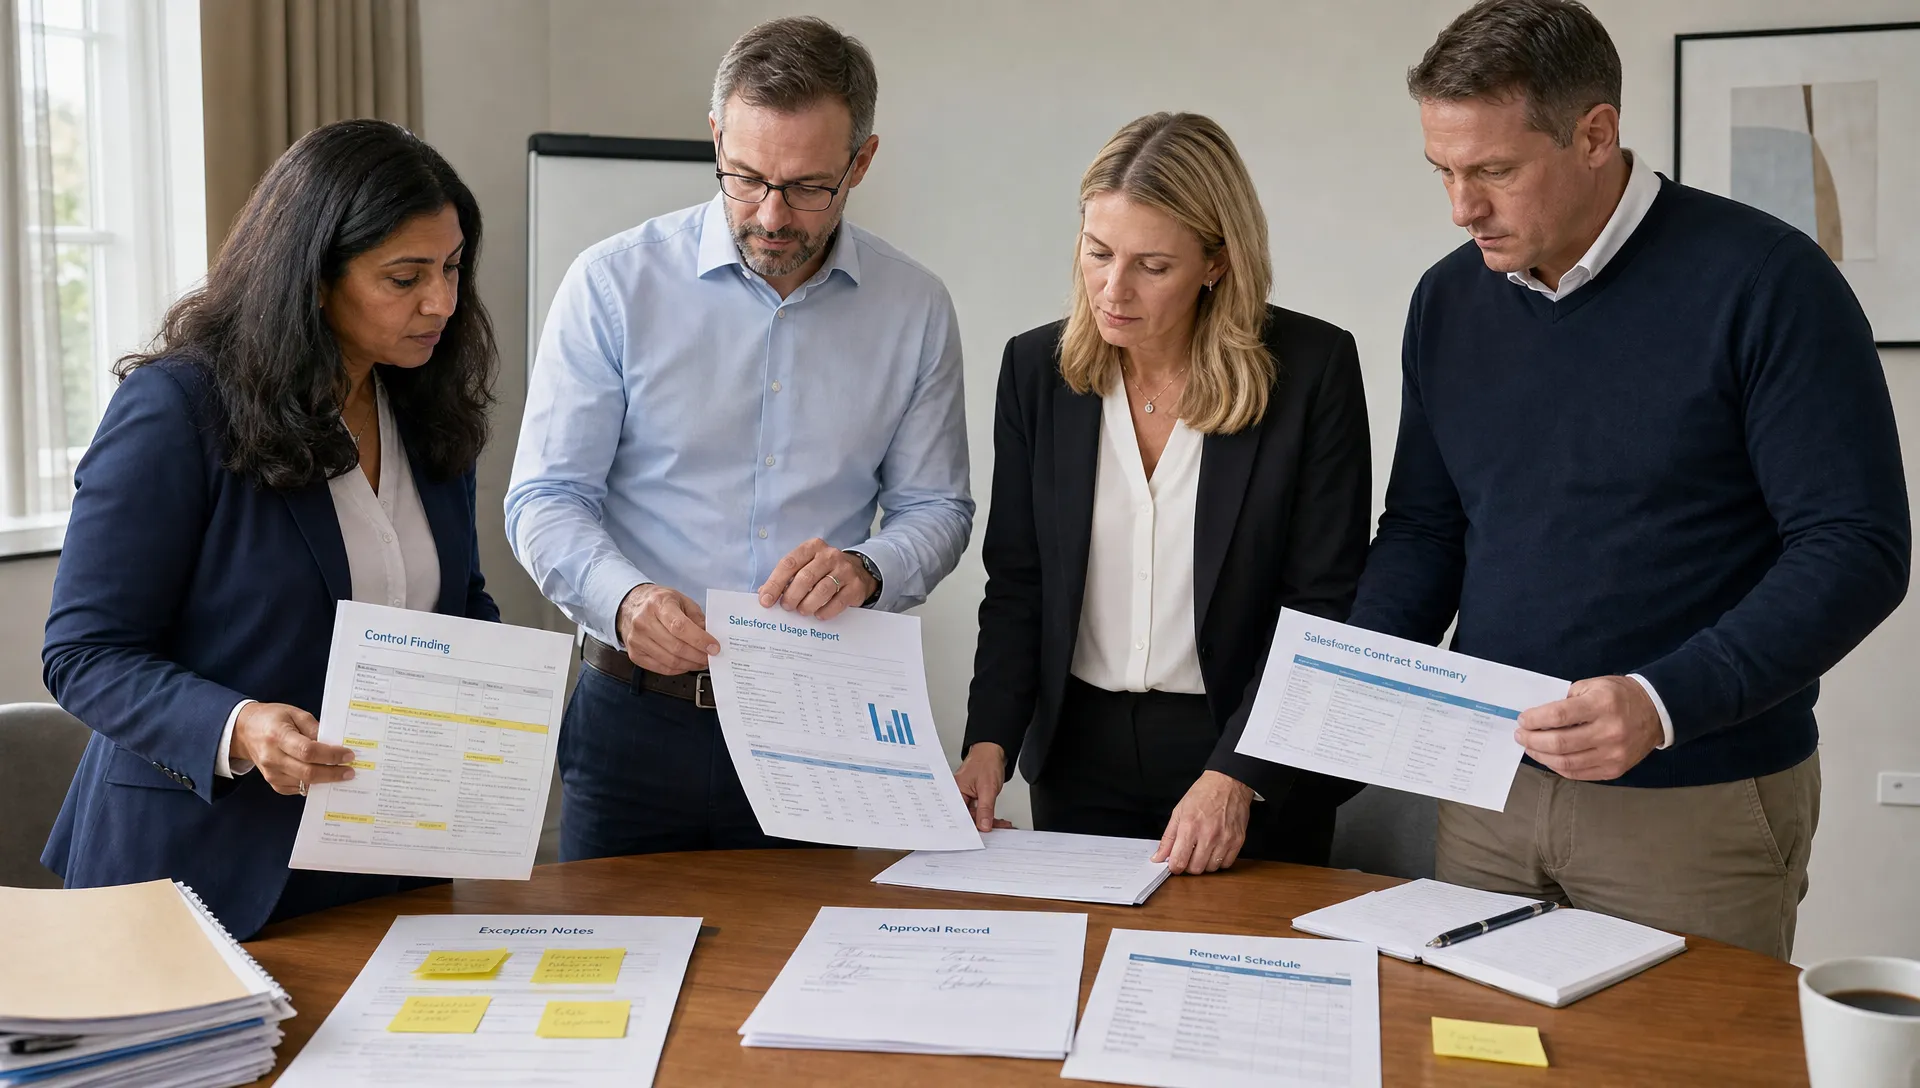
For CFOs, CIOs and procurement leaders, internal audit software is not just a cleaner place to store workpapers. It changes the evidence people trust, the speed at which issues surface and the way oversight bodies challenge decisions, especially when the subject is enterprise SaaS spend.
That matters because audit evidence has moved away from annual folders and static samples. Salesforce estates, SaaS licences, integrations and admin changes all leave digital traces. The question is no longer whether evidence exists. The harder question is whether it is complete, timely, attributable and useful enough to support a decision before renewal pressure arrives.
How internal audit software changes the evidence base
Traditional audit evidence often relies on extracts, screenshots, exported reports and email trails. These can be valid, but they are fragile. A screenshot rarely shows how the report was filtered. An export may not prove who approved the change. An email chain can show discussion without proving that a control operated.
At its best, internal audit software gives those artefacts structure. Evidence can be linked to a control, a risk, an owner, a date, a test result and a finding. That does not make the evidence automatically correct, but it does make it easier to inspect.
The practical shift is from “we have a file” to “we can trace the conclusion”. For Salesforce and SaaS procurement, that traceability is valuable because licence counts, admin rights, role changes and renewal assumptions can all move during the year. Oversight improves when the audit trail and the commercial story are held together rather than reconstructed after the fact.
Evidence becomes time-stamped and attributable
Good evidence has context. It should show when it was captured, what system it came from, who provided it and what question it was meant to answer. Without that context, audit committees and steering groups end up debating the evidence rather than the decision.
This is where systematised evidence handling helps. A user access review, for example, is stronger when the reviewer, source report, exception treatment and approval are all visible in one place. The same applies to a Salesforce SKU review. A licence position is more credible when it can be tied back to contract terms, assigned users, actual usage and business ownership.
In a Salesforce environment, internal audit software can support a cleaner chain of custody for evidence across finance, IT, procurement and business teams. It reduces the temptation to rely on the latest spreadsheet because nobody can find the earlier version.
Exceptions become easier to follow
Most oversight work gets difficult when something does not fit. A control fails. A user has access they no longer need. A department still holds licences for a team that changed structure months ago. A commercial term looks harmless until it is compared with actual usage.
The value is not only in recording exceptions. It is in showing what happened next. Was the issue accepted, remediated or escalated? Who made that judgement? Was there a deadline? Did the issue recur?
That is especially useful for SaaS renewals. If a finding shows unused Salesforce licences, duplicate products or unclear ownership, the next renewal conversation should not treat that as a fresh discovery. It should be part of the evidence base before negotiation planning begins.
Oversight changes when audit data becomes shared
Oversight improves when finance, IT, procurement and internal audit can see the same evidence without collapsing their roles into one another. Finance still tests affordability and value. IT still owns technical fit and operational risk. Procurement still manages supplier leverage and commercial timing. Audit still tests whether the organisation’s controls and assurances are reliable.
This is where internal audit software changes oversight most visibly. It creates a common reference point, but it also exposes where teams disagree. That is healthy. A CIO may see a Salesforce add-on as operationally necessary. A CFO may ask whether adoption supports the cost. Procurement may question whether the renewal structure leaves enough room to negotiate.
The conversation becomes sharper when those views are grounded in the same evidence rather than separate packs.
| Oversight group | What improves | What still needs judgement |
|---|---|---|
| CFO | Clearer link between spend, risk and evidence | Whether the cost is justified by business value |
| CIO | Better visibility of controls, access and change history | Whether the system design fits current needs |
| Procurement | Stronger commercial record before negotiation | How much leverage can realistically be used |
| Internal audit | More consistent testing and follow-up | Whether evidence is sufficient for assurance |
Shared evidence should not mean blurred accountability
A shared evidence base can create a false sense of agreement. Everyone may be looking at the same dashboard, but that does not mean they have reached the same conclusion. Oversight bodies still need clear decision rights.
For example, procurement may identify renewal leverage because adoption is lower than forecast. IT may still need some unused capacity for a planned rollout. Finance may agree to keep part of the estate but reject a multi-year expansion. Internal audit may simply record whether the decision was made on complete and reliable evidence.
Those distinctions matter. Software can show the facts more clearly, but it should not soften the accountability for interpreting them.
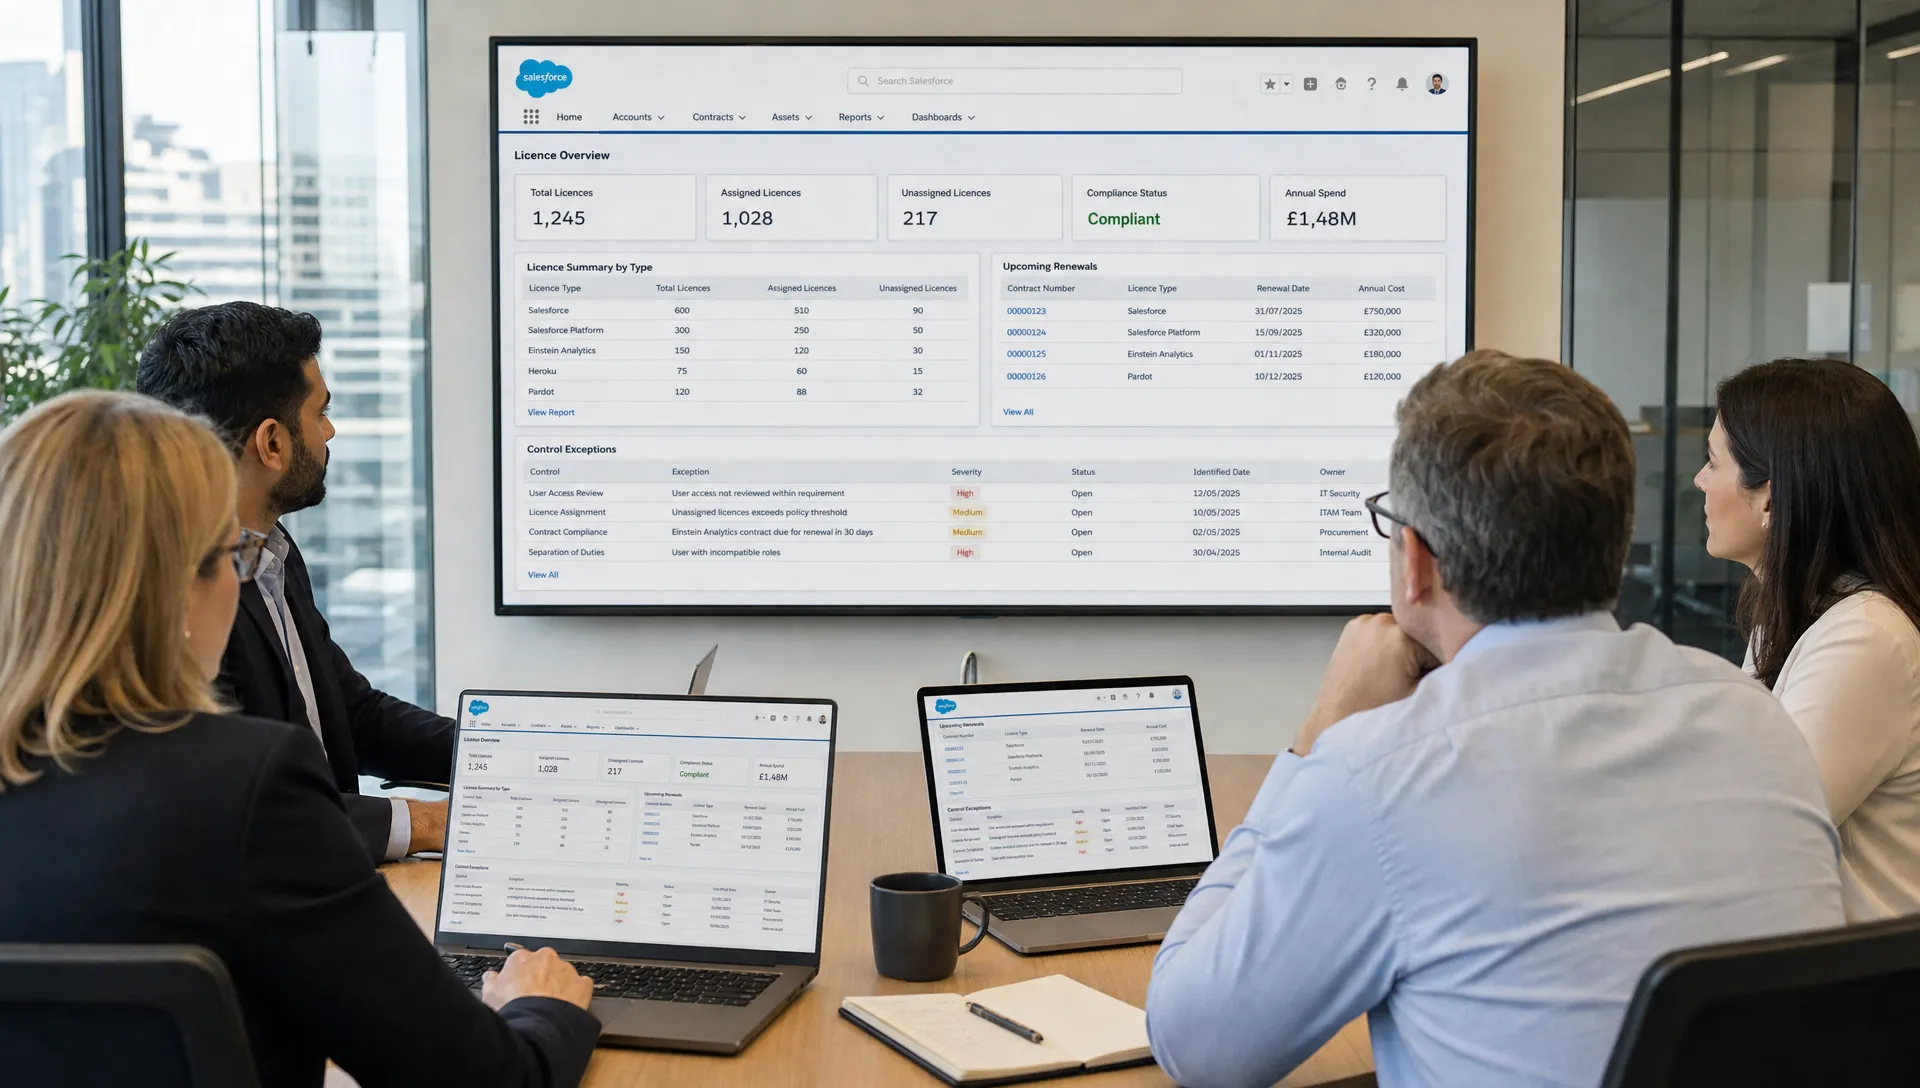
Why Salesforce evidence needs commercial context
Salesforce is not a single line item for many organisations. It can include multiple clouds, editions, add-ons, support levels, sandbox entitlements, integrations and contract-specific terms. Evidence about controls or usage becomes more useful when it is mapped to that commercial reality.
For CFOs, internal audit software can make SaaS evidence easier to challenge, but only if the data model reflects how the contract is actually built. A user count without SKU detail is incomplete. A login report without licence type can be misleading. A renewal forecast without shelfware analysis can protect the wrong spend.
That is why audit evidence and procurement evidence need to meet earlier. If internal audit finds weak joiner, mover and leaver controls, that may have licence implications. If procurement finds unused licences, that may point to weak governance, unclear ownership or outdated business assumptions.
SaaSed has written separately about what a software audit should find before renewal, but the oversight point is simpler: the evidence should explain both risk and money.
Audit trails are useful, but they are not the full truth
Salesforce provides native ways to inspect administrative activity. For example, the official Salesforce Setup Audit Trail documentation explains how teams can monitor setup changes. This can be valuable evidence for access, configuration and change management reviews.
But an audit trail does not automatically answer the commercial question. It may show that a permission set changed, but not whether the related licence is still needed. It may show that a feature is configured, but not whether the business uses it enough to justify renewal.
That is the gap oversight teams need to close. Technical evidence should be joined with contract evidence, usage evidence and decision evidence. Otherwise, the organisation may pass a control test while still carrying avoidable spend.
Where the software can mislead oversight
Good internal audit software can still produce poor oversight if the scope is wrong. A polished workflow cannot rescue incomplete inputs. A dashboard can make weak evidence look settled. Automated reminders can close actions that were never properly resolved.
This is a particular risk in SaaS estates because the numbers can look precise. Licence quantities, usage percentages, inactive users and contract dates all appear measurable. The danger is assuming measurable means meaningful.
Before relying on the output, oversight teams should ask what the system is not showing. Does it include all Salesforce contracts or only the current order form? Does usage data cover meaningful activity or just logins? Are add-ons and bundles visible? Has procurement captured renewal notice periods, co-terming effects and commercial commitments?
For a deeper view on hidden spend patterns, the SaaSed guide to where audit and compliance software costs hide is a useful companion piece.
| Risk in the evidence | How it affects oversight | Better question to ask |
|---|---|---|
| Login data used as usage proof | Active users may still create little value | What business process does the user perform? |
| Contract terms not mapped to SKUs | Spend cannot be linked to entitlement | Which products and limits are we actually renewing? |
| Exceptions closed without proof | Remediation may be overstated | What evidence shows the issue was fixed? |
| Audit scope too narrow | Renewal risk sits outside the review | Which systems, add-ons and teams are excluded? |
Independence still matters
The Institute of Internal Auditors’ Global Internal Audit Standards place strong emphasis on independence, objectivity and quality. Software does not change that duty.
If the same team that owns the system also defines the evidence, tests the evidence and declares the issue closed, oversight becomes weaker. That does not mean every review needs an external party. It means the organisation should be honest about where conflicts of interest may sit.
In a Salesforce renewal, independence might be as simple as asking procurement to test commercial assumptions, finance to test value assumptions and IT to test operational assumptions. Internal audit can then assess whether the evidence and decision process are robust enough.
How to set up evidence before renewal pressure starts
Before buying or expanding internal audit software, agree what decisions the evidence must support. This avoids the common mistake of designing an elegant audit workflow that does not help when a renewal, budget challenge or supplier negotiation arrives.
For Salesforce-heavy organisations, the starting point is usually a small set of decision questions. What are we entitled to use? What are we actually using? Which licences are underused or misaligned? What contract terms constrain our options? Which risks are we willing to accept and which need action before renewal?
If you are still shaping the tool scope, SaaSed’s article on choosing compliance audit software without buying too much covers a related buying discipline: start with the evidence you need, not with the longest feature list.
A practical evidence checklist
A disciplined evidence model does not need to be elaborate. It needs to be clear enough for scrutiny.
- Contract baseline, including order forms, amendments, renewal dates and notice periods
- SKU and entitlement map, matched to the way Salesforce products are actually billed
- Usage evidence that separates logins from meaningful business activity
- Ownership record for each major product, add-on and integration
- Exception log showing findings, decisions, remediation evidence and accepted risk
- Renewal evidence pack that finance, IT, procurement and audit can all inspect
This checklist helps keep oversight grounded. It also stops renewal preparation becoming a scramble for old exports and half-remembered decisions.
What changes for CFOs, CIOs and procurement leaders
The main change is not technical. It is behavioural. Evidence becomes harder to ignore and easier to challenge.
For CFOs, the benefit is a clearer line between assurance, spend and value. If a Salesforce product is renewed, there should be evidence that the cost is still defensible. If spend is reduced, there should be evidence that the operational risk is understood.
For CIOs, the benefit is cleaner control visibility. Access reviews, configuration changes, integration ownership and remediation actions can be shown with more discipline. That helps IT defend necessary investment and acknowledge areas where controls need work.
For procurement leaders, the benefit is timing. Internal audit software can bring renewal-relevant evidence into view before the supplier conversation narrows the room for manoeuvre. Better evidence does not guarantee a better commercial outcome, but weak evidence almost always reduces leverage.
Frequently Asked Questions
Does internal audit software replace internal auditors? No. It can organise evidence, automate workflows and improve follow-up, but it does not replace judgement, independence or challenge. Auditors still need to decide whether the evidence is sufficient and what it means.
How does audit software help with Salesforce renewals? It can help teams collect and structure evidence on usage, access, ownership, exceptions and control gaps. That evidence becomes more valuable when it is linked to contract terms, SKU entitlements and renewal timing.
What evidence is most often missing before a SaaS renewal? The common gaps are clean SKU mapping, meaningful usage data, proof of business ownership, accepted risk decisions and a record of why previous renewal choices were made.
Can audit software reduce Salesforce spend by itself? No. The software can reveal evidence that supports better decisions, but savings depend on contract analysis, usage review, internal alignment and negotiation strategy.
Who should own the evidence model? Internal audit may own the assurance approach, but finance, IT and procurement should all shape the evidence model. Each team sees a different part of the risk and value picture.
Conclusion: better evidence, calmer oversight
Internal audit software changes evidence by making it more traceable, structured and available for challenge. It changes oversight by giving CFOs, CIOs, procurement and audit teams a shared base for decisions without removing their separate responsibilities.
For Salesforce estates, the value is strongest when audit evidence is connected to commercial evidence. Usage, controls, licences, SKU fit and renewal terms need to be read together. Otherwise, the organisation may have a tidy audit file and still enter renewal talks with avoidable uncertainty.
If your next Salesforce renewal needs a cleaner evidence base, SaaSed can help review contracts, SKUs, usage and commercial risk before negotiations begin. You can book a complimentary Salesforce audit conversation to see where the evidence is strong, where it is thin and what should be fixed before the renewal window tightens.
Want this kind of intel on your renewal?
Don’t head into your next software negotiation alone
Contact Us